Chapters
0:00 The Hacker Windows Caught
0:26 The Experiment: Fresh Windows in Proxmox
0:40 Finding the VM Interface
1:27 Capturing with tcpdump
1:53 The Auto-Capture Script
3:11 Pulling the PCAP and Opening Wireshark
3:51 Filtering for SNI: Where Windows Phones Home
4:15 Easier Analysis with SO-CRATES
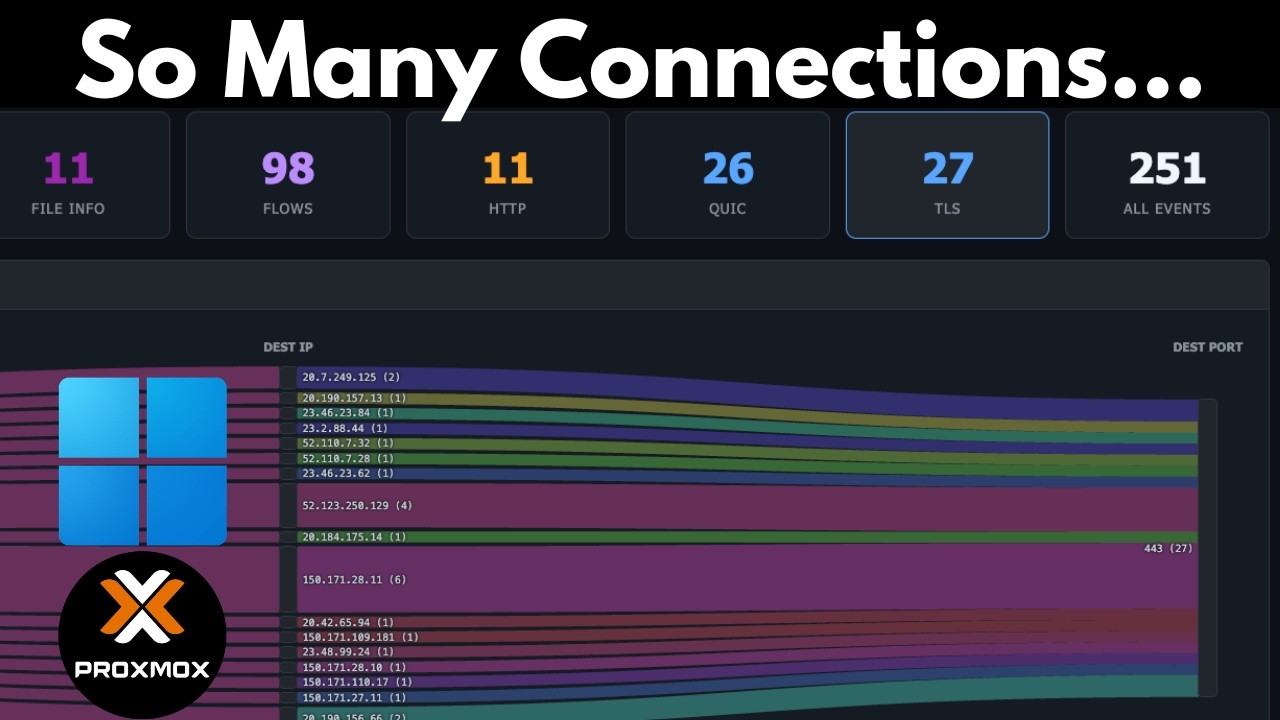
5:03 Reading the Results: DNS, HTTP, TLS
6:12 The EFF Shirt and Can You Block It?
7:51 Why I Trust Linux More
8:00 Wrap-Up
As Tom said, everything you do at OS level can be reverted later by windows update. There are several things you can do at network level, but thats also not a reliable solution because windows update can change network destinations as well, and get around whatever you have setup on your network. Just dont use windows.
Thanks Tom, I didn’t need to use proxmox to see the network flow I just did a filter in the flows in the Unifi dashboard and filtered on my Windows PC. I am also publishing flows to visualize them in GrayLog and have a nice dashboard setup.
Without actual testimonials or reports such as this one, all pieces of information remains speculation. I therefore very much support and appreciate such journalism which uncovers the actual consequences of such data collection and @LTS_Tom for extending the awareness even further.

 Tom🌶\(^-^)/🌶 infosec.exchange/@tomlawrence (@TomLawrenceTech) / X

 Lawrence Systems's Amazon Page
 https://www.patreon.com/lawrencesystems