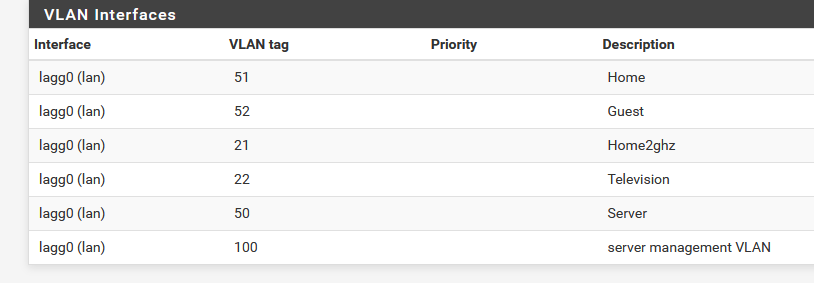
I’ve started segmenting my network with VLANs. Any time I try to assign port “VLAN 11 on lagg0” to my “LAN” interface pfSense GUI becomes unresponsive even when I plug into an access port on VLAN 11. It seems as though device changes to LAN is problematic. When I reboot pfSense the old interface is selected.
Is it more common to just abandon the default “LAN” interface for VLANS. What do you do with LAN once all of your segments are configured and running? I would basically want to move my entire LAN configuration to VLAN 11. I read somewhere that pfSense still needs the LAN interface for some of the services to work correctly.
pfSense: 2.8.0
Unifi USW-24-POE: 9.1.120
Do the change while you are connected to pfSense via another interface, which is not changed at all.
I am not sure if my approach is the best or even proper, but I do not put any VLAN on the LAN interface.I do create a LAGG first on the LAN interface but then I create new interfaces for each VLAN. Then I create firewall rules for each interface to segregate them as I wish, I leave LAN as the default VLAN of 1
That is almost exactly how I’ve done things. I’ve done some reading that it is against best practice to use VLAN1 because all untagged traffic on a trunk port end up on VLAN1. The risk is if someone manages to plug into a trunk port they can VLAN hop. This really isn’t a problem at home but I’m trying to learn best practice.
That’s true, but every VLAN needs a parent interface. If you assign a VLAN to the LAN port, what is going to be the parent interface? I am not sure you need to change the default VLAN for your LAN interface. Rather, you need to make sure you don’t use VLAN1 in your switch for the management interface. Notice the Netgate documentation on VLAN1 and security is all about the switch configuration